How to connect Doppler SecretOps to OpenClaw
Connect Doppler SecretOps to OpenClaw with ClawLink: paste your Doppler SecretOps key once and 29 tools work from chat. No MCP server to run, nothing stored on your machine.
 Doppler SecretOpsAPI KEYMCP
Doppler is a secrets management platform that helps teams securely manage and sync environment variables across projects and environments.. Once connected, OpenClaw can read and act on Doppler SecretOps from chat — pairing, token refresh, and tool wiring handled for you.
The usual route to Doppler SecretOps access for OpenClaw is an MCP server you configure and keep running, plus your own OAuth app or API keys. ClawLink gives OpenClaw a more practical Doppler SecretOps setup: install one ClawHub skill, connect Doppler SecretOps in the browser, and OpenClaw can call real Doppler SecretOps actions from any chat surface with no auth, token refresh, or tool wiring to build yourself.
Setup
It takes three steps to connect OpenClaw to Doppler SecretOps.
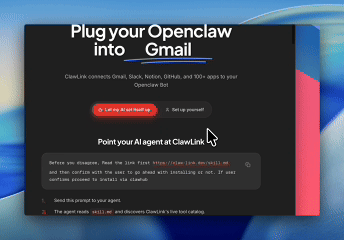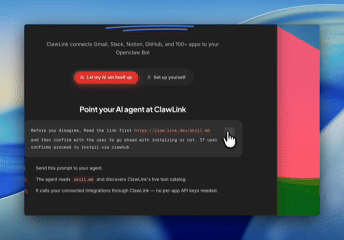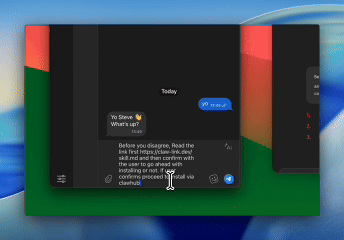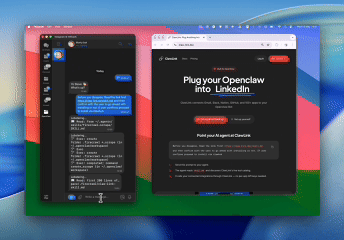 1
Install the plugin
Paste the setup prompt into OpenClaw, or install from the terminal and ask OpenClaw to pair:
openclaw plugins install clawhub:clawlink-plugin- 2
Connect Doppler SecretOps
Paste your API key in the dashboard.
- 3
Use it from chat
Ask OpenClaw: "What can you do with Doppler SecretOps?"
Install by command
The setup prompt above does all of this in one paste. By hand, it is one install command plus a browser approval:
openclaw plugins install clawhub:clawlink-pluginThen ask OpenClaw to set up ClawLink. It starts browser pairing and prints an approval link — open it, approve the device, return to the chat, and say done. Finally, connect Doppler SecretOps in the ClawLink dashboard — paste your Doppler SecretOps API key once.
Verify the connection by asking OpenClaw:
Use Doppler SecretOps to activity logs list and walk me through the result in plain English.
Using a different agent?
The OpenClaw plugin is one client of ClawLink's MCP server. Claude Code, Cursor, Codex, or any agent that can run a shell command pairs with the same ClawLink account through the CLI:
npx -y @useclawlink/cli loginlogin opens the same browser approval and stores a credential locally. Once Doppler SecretOps is connected in the dashboard, that agent calls the same 29 Doppler SecretOps tools over MCP. Full setup for MCP clients and shell agents: connect apps to any AI agent.
Doppler SecretOps MCP for OpenClaw
Looking for a Doppler SecretOps MCP server for OpenClaw? ClawLink connects Doppler SecretOps to OpenClaw and exposes 29 Doppler SecretOps tools your agent can call over MCP, with hosted auth and nothing to run or maintain yourself. Using Hermes instead? The Hermes Doppler SecretOps integration works the same way.
What the OpenClaw Doppler SecretOps integration can do
29 Doppler SecretOps tools are ready for OpenClaw once the account is connected. The 24 below are the ones people reach for most; your agent can call all 29.
24 of 29 Doppler SecretOps tools for OpenClaw
| Tool | What it does |
|---|---|
Activity logs list doppler_secretops_activity_logs_list | List workplace activity logs |
Activity logs retrieve doppler_secretops_activity_logs_retrieve | Retrieve a single activity log entry by id |
Config logs get doppler_secretops_config_logs_get | Retrieve a specific config log entry |
Config logs list doppler_secretops_config_logs_list | List config change logs for a specific config |
Configs get doppler_secretops_configs_get | Fetch a config's details |
Environments get doppler_secretops_environments_get | Retrieve an environment |
Environments list doppler_secretops_environments_list | List environments in a Doppler project |
Integrations list doppler_secretops_integrations_list | List all external integrations |
Invites list doppler_secretops_invites_list | List open workplace invites |
Project members get doppler_secretops_project_members_get | Retrieve a project member by type and slug |
Project permissions list doppler_secretops_project_permissions_list | List project-level permissions |
Project roles get doppler_secretops_project_roles_get | Retrieve a project role |
Projects list doppler_secretops_projects_list | List Doppler projects |
Config logs rollback doppler_secretops_config_logs_rollback | Rollback a config to a selected log version |
Configs clone doppler_secretops_configs_clone | Clone a branch config including all its secrets |
Configs create doppler_secretops_configs_create | Create a branch config |
Configs lock doppler_secretops_configs_lock | Lock a config |
Configs unlock doppler_secretops_configs_unlock | Unlock a config |
Configs update doppler_secretops_configs_update | Modify an existing config |
Environments create doppler_secretops_environments_create | Create a new environment |
Environments rename doppler_secretops_environments_rename | Rename an environment |
Projects create doppler_secretops_projects_create | Create a project |
Secrets update doppler_secretops_secrets_update | Update secrets in a config |
Dynamic secrets revoke lease doppler_secretops_dynamic_secrets_revoke_lease | Revoke a dynamic secret lease |
Try it: find the Doppler SecretOps tool you need
Browse the 24 Doppler SecretOps tools
Click any tool to see exactly what OpenClaw can do and copy a ready-to-use prompt.
Example prompts
Use Doppler SecretOps to activity logs list and walk me through the result in plain English.
Use Doppler SecretOps to activity logs retrieve and walk me through the result in plain English.
Use Doppler SecretOps to config logs get and walk me through the result in plain English.
Use Doppler SecretOps to config logs list and walk me through the result in plain English.
ClawLink vs. building it yourself
The alternative to ClawLink is usually manual API key setup plus your own token handling, permission troubleshooting, and tool plumbing for OpenClaw. That is fine if you want to build and maintain the integration yourself. Most teams just want Doppler SecretOps working from chat.
| Manual | ClawLink | |
|---|---|---|
| Credential handling | Collect, validate, store, and rotate the Doppler SecretOps API key yourself, then make sure every tool call uses the right account. | Users complete the hosted ClawLink setup once and the connected Doppler SecretOps account becomes available to the agent without you building credential management. |
| Ongoing maintenance | You own refresh logic, permission debugging, environment config, and every provider-specific edge case for Doppler SecretOps. | ClawLink handles the repetitive integration plumbing so your team can focus on the workflow instead of the infrastructure. |
| Agent usability | You still need to expose the right Doppler SecretOps actions to the runtime in a format your agent can reliably use. | 29 tools for Doppler SecretOps are already exposed through ClawLink, so the agent can read and act from chat immediately. |
ClawLink vs. Composio
Composio also exposes Doppler SecretOps to AI agents. It is developer infrastructure: Python and TypeScript SDKs, an MCP server, and a catalog past 1,000 apps, aimed at teams shipping agent products. ClawLink is built for OpenClaw users instead. You install the plugin once, connect Doppler SecretOps in the browser, and the 29 tools above work from chat. There is no SDK and no config file, and the Doppler SecretOps key you paste at setup is stored server-side rather than kept in your environment. Choosing between them? Read the full Composio alternatives comparison.




Troubleshooting
OpenClaw installed the Doppler SecretOps skill but can't call the tools
The ClawHub skill teaches OpenClaw about Doppler SecretOps, but the calls run through the ClawLink plugin and your connected account. Make sure Doppler SecretOps is connected in the dashboard, then start a fresh chat so OpenClaw reloads the tool catalog. If OpenClaw runs as a persistent gateway, restart it so the new tools register.
Connection succeeds but no tools appear
Reconnect Doppler SecretOps from the dashboard, then start a fresh chat if the runtime still has the old tool catalog loaded.
"Tool schema not loaded yet" error when calling Doppler SecretOps tools
Doppler SecretOps tool schemas load on demand the first time a tool runs and are cached after that, so this error usually clears on its own: wait a few seconds and retry the same request. If every Doppler SecretOps call keeps failing with it in a fresh chat, reconnect from the dashboard, and contact support if it still persists — that pattern points to a configuration problem on our side, not something you can fix by reconnecting again.
Doppler SecretOps returns 403 or "permission denied" on one action while others work
Two usual causes. The connected account may not have access to the specific workspace, inbox, store, or project in the request — check that first. If access looks right, the agent may have sent a placeholder value (like "YOUR_ID" or an example id from documentation) instead of a real one: ask it to run a list or search tool first, then retry the action with a real id from those results. Most failures at this stage are one of these two, not ClawLink bugs.
API key setup works but results look incomplete
Double-check that the API key for Doppler SecretOps has the right scopes or account access. A valid key can still be too limited for some reads or writes.
FAQ
Is there a OpenClaw Doppler SecretOps integration?
Yes. ClawLink is the fastest way to connect OpenClaw to Doppler SecretOps: link your Doppler SecretOps account once in the browser and OpenClaw can call the Doppler SecretOps API through 29 ready-made tools — no custom code or token handling.
How do I add Doppler SecretOps to OpenClaw with ClawLink?
Paste the setup prompt from this page into OpenClaw. It installs the ClawLink Doppler SecretOps skill from ClawHub, then you click Connect in the dashboard to authorize Doppler SecretOps. OpenClaw calls the tools from the next message — no config files, and the Doppler SecretOps key you paste is stored server-side instead of in your environment.
How long does it take to connect Doppler SecretOps to OpenClaw?
About two minutes. Sign in, click Connect next to Doppler SecretOps in the dashboard, authenticate, and OpenClaw can use it from the next chat message.
Why use ClawLink instead of wiring Doppler SecretOps up myself?
The alternative to ClawLink is usually manual API key setup plus your own token handling, permission troubleshooting, and tool plumbing for OpenClaw. That is fine if you want to build and maintain the integration yourself. Most teams just want Doppler SecretOps working from chat.
OpenClaw installed the Doppler SecretOps skill but can't call the tools
The ClawHub skill teaches OpenClaw about Doppler SecretOps, but the calls run through the ClawLink plugin and your connected account. Make sure Doppler SecretOps is connected in the dashboard, then start a fresh chat so OpenClaw reloads the tool catalog. If OpenClaw runs as a persistent gateway, restart it so the new tools register.
Related
OpenClaw GitHub integration
Manage repositories, issues, pull requests, and workflows

PagerDuty tools
Manage incidents, on-call schedules, and services

OpenClaw SafetyCulture integration
SafetyCulture (formerly iAuditor) is a workplace operations platform that enables teams to conduct digital inspections, manage audits, track issues, schedule tasks, and maintain compliance through mobile and web applications.